20 Oct Microsoft Is Retiring SMS and Voice MFA: What Wisconsin Businesses Need to Do Before 2027
The short answer
On February 1, 2027, Microsoft will stop sending text message (SMS) and phone call codes for multi-factor authentication (MFA) in Microsoft 365. Any employee who still signs in with a texted or phoned code will be forced to set up a passkey before they can get into their email, Teams or files.The change is already underway. Since September 1, 2026, Microsoft has been prompting SMS and voice users to register a passkey every time they sign in. That leaves Wisconsin businesses less than four months to move their people to stronger sign-in methods, or risk a Monday morning full of locked-out staff.The good news: if your team already uses the Microsoft Authenticator app, a security key or Windows Hello, nothing changes for them. This post explains what is changing, the full timeline, and the five steps to take now.
What is Microsoft changing?
Microsoft is shutting down the free, built-in service that texts or calls your employees with a one-time sign-in code. This lives in Microsoft Entra ID, the identity system behind every Microsoft 365 business account.Two things are happening at once:Passkeys become the default. A passkey is a sign-in credential stored on your phone, laptop or a physical security key. You unlock it with your face, fingerprint or PIN. There is no code to type and nothing for a scammer to steal.Microsoft-provided SMS and voice codes retire. After the cutoff, Microsoft will no longer deliver those codes for MFA or for self-service password reset.MFA itself is not going away. Microsoft is replacing its weakest MFA option with stronger ones.
The SMS and voice MFA retirement timeline
The key date is February 1, 2027. Global Administrators and external users get a short extension to July 1, 2027. Here is every milestone and what it means for your business.
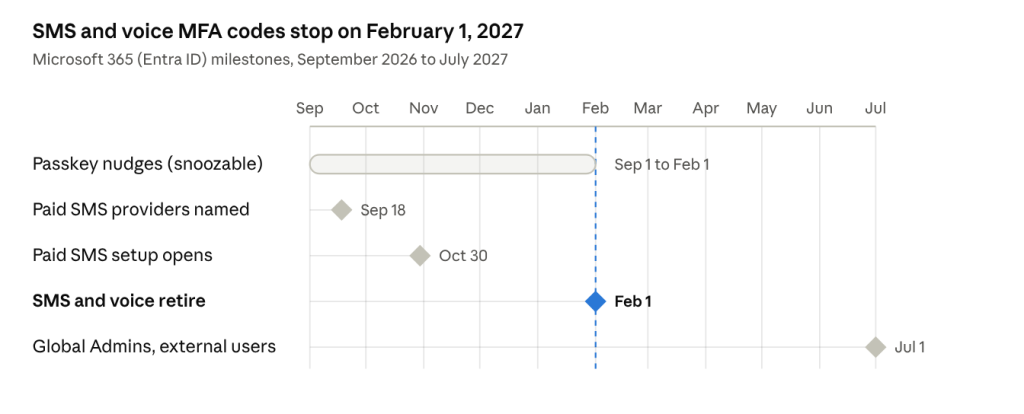
SMS and voice MFA retirement timeline · 5 milestonesUntil February 1, staff can keep snoozing the passkey prompt. After that date, setup is mandatory.
Why is Microsoft retiring SMS and voice MFA?
Text and phone codes are now among the easiest MFA methods for criminals to beat. Microsoft calls SMS and voice some of the most vulnerable authentication methods available today (Microsoft Learn).Three attacks do most of the damage:SIM swapping. A scammer talks your mobile carrier into moving your number to their phone. Your codes now go to them.Phishing for the code. A fake Microsoft login page asks for your password, then asks for the texted code. The attacker types both into the real site in seconds.AI-powered social engineering. Microsoft's 2025 Digital Defense Report found AI-written phishing emails got a 54% click-through rate, versus 12% for human-written ones (The Register).A passkey stops all three. It is tied to your device and only works on the real Microsoft website, so there is no code to forward and nothing a fake login page can capture.
You are affected if even one person in your Microsoft 365 tenant is enabled for SMS or voice sign-in. That includes users switched on in older "per-user MFA" settings, which many small businesses still have running in the background.
Personal Microsoft accounts, like Outlook.com, are moving toward passkeys too, but this deadline is for business accounts.